Workshop: From Attack to Defense: A Series of Cybersecurity Workshops with Specialists from IstroSec
Workshop: From Attack to Defense: A Series of Cybersecurity Workshops with Specialists from IstroSec
The Faculty of Management Science and Informatics, in cooperation with IstroSec, has prepared a series of six practical workshops primarily intended for students interested in cybersecurity, ethical hacking, and penetration testing. The workshops follow an attacker’s journey step by step, from reconnaissance and gaining access to moving through a network, all the way to detection and defense. Each workshop combines expert instruction with hands-on LAB sessions in a realistic environment.
When: starting October 6, 2026, every Tuesday from 2:00 PM to 6:00 PM (6 weeks)
Where: RB303
Registration: link by October 2, 2026
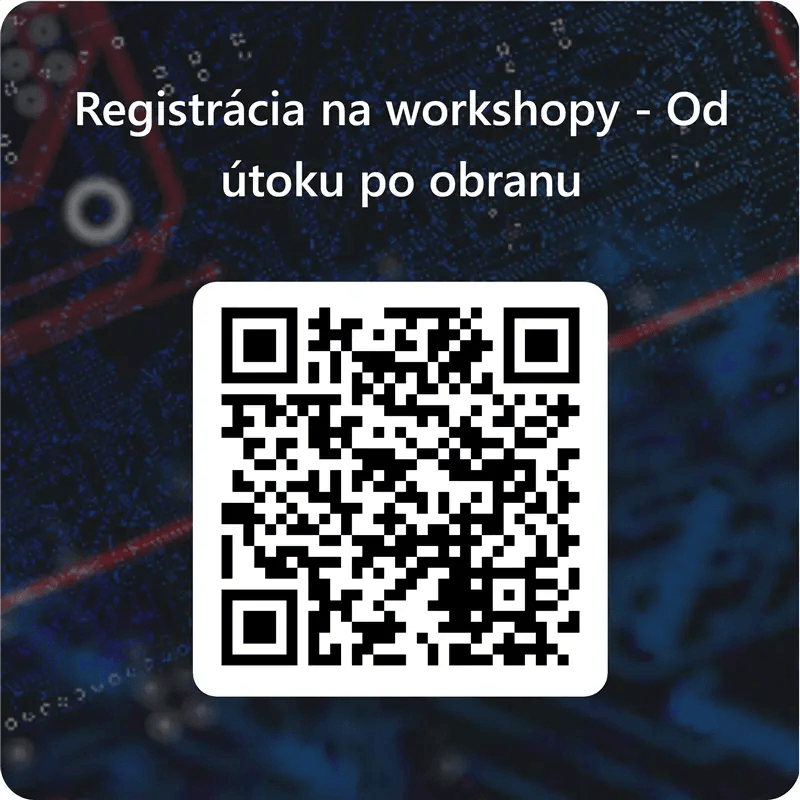
Registration is valid for the entire series of six workshops, not for individual sessions, as the topics build on one another. Capacity is limited to 16 participants.
Workshop Program
1. Reconnaissance and Mapping the Organization’s Attack Surface
Passive data gathering from public sources (OSINT), identification of the attack surface, and mapping of external infrastructure. The workshop also explains how credential leaks occur and how stolen credentials are traded on the Dark Web.
2. Web Application Penetration Testing
The most common vulnerabilities according to the OWASP Top 10 and working with a web proxy (Burp Suite), including capturing, analyzing, and modifying HTTP/HTTPS traffic. Practical testing of vulnerabilities such as XSS, SQL Injection, SSRF, and IDOR.
3. Network Reconnaissance and Scanning
Passive and active techniques for mapping network infrastructure, identifying devices, ports, and services, host enumeration, and detecting outdated and vulnerable systems.
4. Initial Access and Exploitation
How a vulnerable service can become a real entry point into a system. Remote code execution, context, and user privileges after exploitation.
5. Privilege Escalation, Lateral Movement, and Persistence
The attacker’s steps after gaining access to internal infrastructure, privilege escalation, obtaining and exploiting credentials, lateral movement, pivoting, and techniques for maintaining access.
6. Purple Team Exercise
A final integration of the knowledge gained throughout the workshops. The red team performs attack phases based on the MITRE ATT&CK framework, while the blue team detects and blocks them in real time. The session also includes a discussion of countermeasures and a demonstration of the capabilities of the Gryphon EDR solution.
Co-financed by the European Union through the Slovakia Programme under project No. NFP401101C360: Research and development of advanced artificial intelligence solutions for the detection of cyber threats and defense against sophisticated attacks.